
Tangent Technologies · Solutions
Security operations that explain themselves.
The Tangent AI Security Console runs autonomous triage, continuous compliance, and true-coverage vulnerability management across your live Microsoft 365, Defender, and Wazuh estate, and shows its work for every decision it makes.
The premise
Most security stacks lie by omission.
- A sensor badge reads “no data” while the endpoint ships thousands of real events a day.
- A device with zero findings quietly drops out of the inventory, so the healthiest machine looks like a blind spot.
- The same fact lives in five dashboards and they disagree with each other.
- Tangent resolves one auditable answer from live telemetry, and flags the signal that was lying.
Capabilities
One console across the work a security team actually does.
Detection, investigation, compliance, and exposure: operated by AI agents with deterministic guardrails, and reviewable end to end.
Autonomous SOC analyst
Triages alerts, builds the case, and dispositions it against live Defender and Microsoft 365 context: benign closed with evidence, real threats escalated with a quarantine recommendation, nothing left silently open.
Triage · Case lifecycle
Detection-to-Hunt loop
Every confirmed detection spawns a scoped, rule-agnostic hunt and closes it when the source case goes terminal, so investigation compounds into coverage instead of dying in a ticket.
Proactive hunting
Continuous compliance
CMMC Level 2, ISO 27001, and NIST SP 800-171 controls evidenced from your real Entra, Defender, Azure, and Wazuh state, not a spreadsheet of attestations. Insufficient evidence is said plainly, never faked.
CMMC L2 · ISO 27001 · 800-171
True-coverage vulnerability management
Per-device vulnerability collection that counts every onboarded endpoint (including the finding-free ones legacy exports silently drop) with a coverage guard that alarms on gaps instead of hiding them.
No silent drops
Asset & EDR intelligence
A unified inventory that unions your managed registry, Defender device inventory, and live Wazuh agents, with EDR liveness derived from actual event flow (not a stale health badge) and every device resolved to an owner.
Liveness from telemetry
Evidence custody & audit chain
Decisions, approvals, and the evidence behind them are recorded in a tamper-evident chain, so an auditor, a customer questionnaire, or a 2 a.m. incident review can all trace exactly why the system did what it did.
Defensible by design
Inside the console
The answer, and the evidence behind it, on one screen.
Real console views, with identifiable data redacted for the web. Every number traces back to a live source your team can click into.
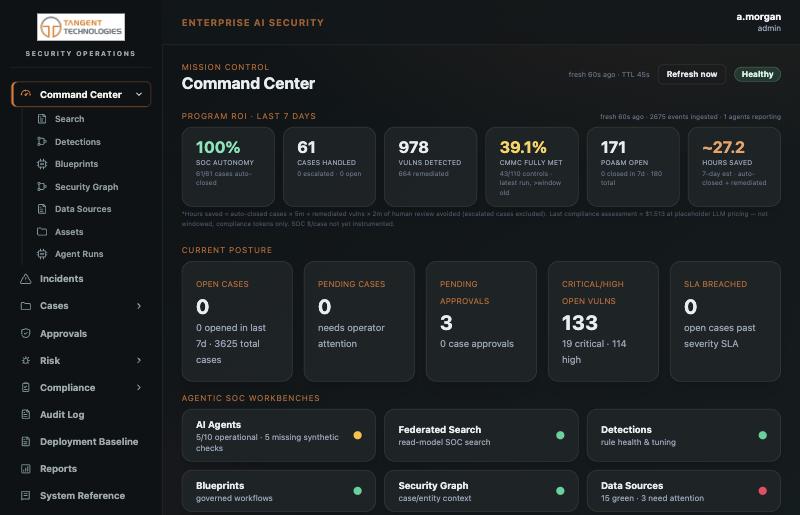
One command center. Autonomy rate, cases, exposure, CMMC coverage, and connector health: the whole program at a glance, each tile a live source.
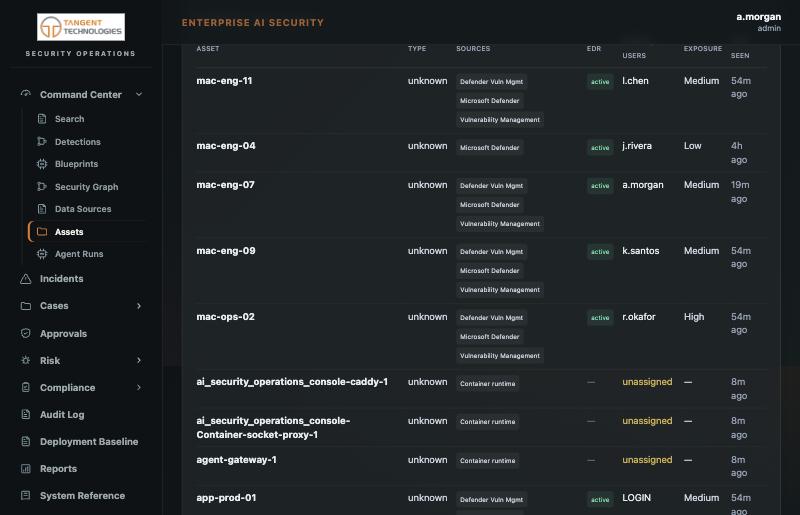
Asset & EDR intelligence. Liveness read from real event flow, with every device resolved to an owner. A stale “no sensor data” badge is flagged, not trusted.
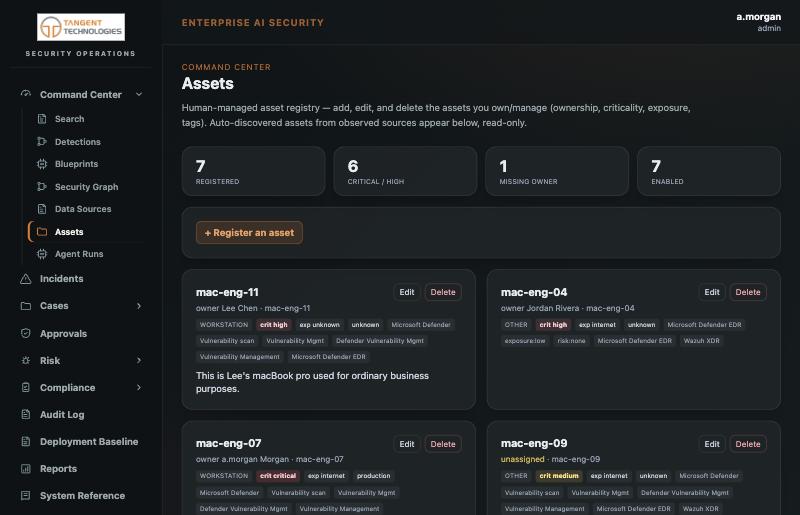
Unified inventory. Managed registry and auto-discovered assets in one place: criticality, exposure, and every source that observed the device.
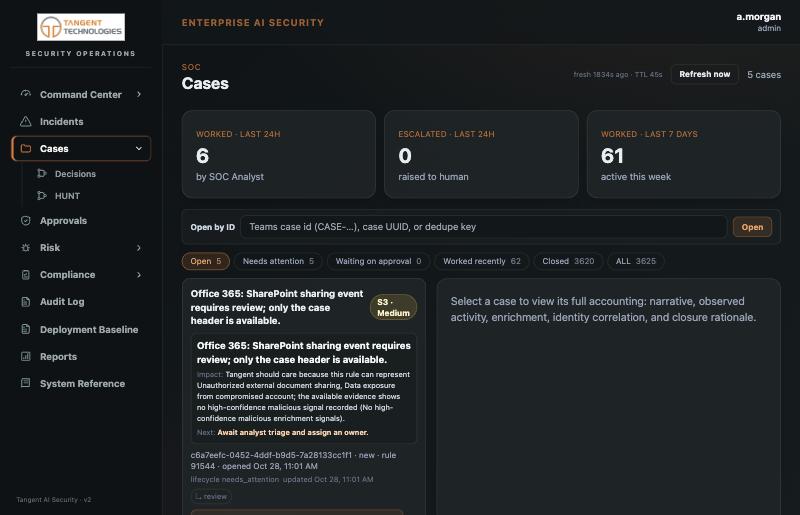
Autonomous SOC analyst. Triaged with impact and next action, lifecycle tracked: benign closed with evidence, real threats raised to a human.
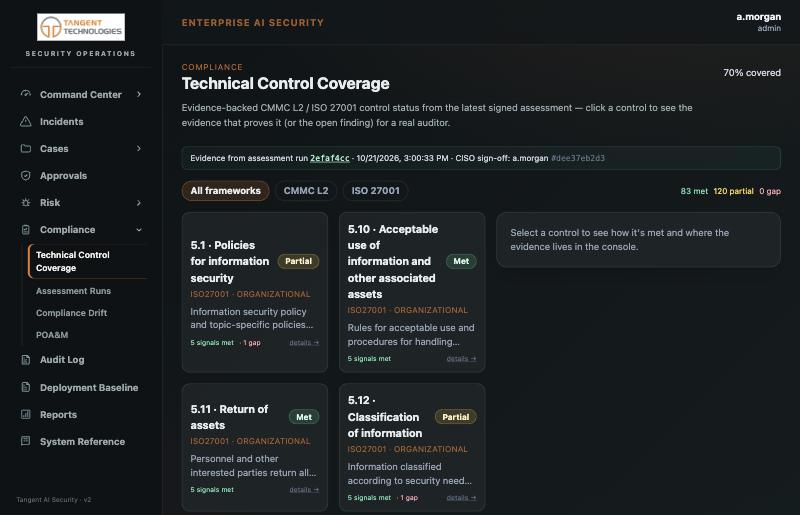
Continuous compliance. CMMC L2 and ISO 27001 controls evidenced from live state, and marked “insufficient evidence” rather than invented when proof is missing.
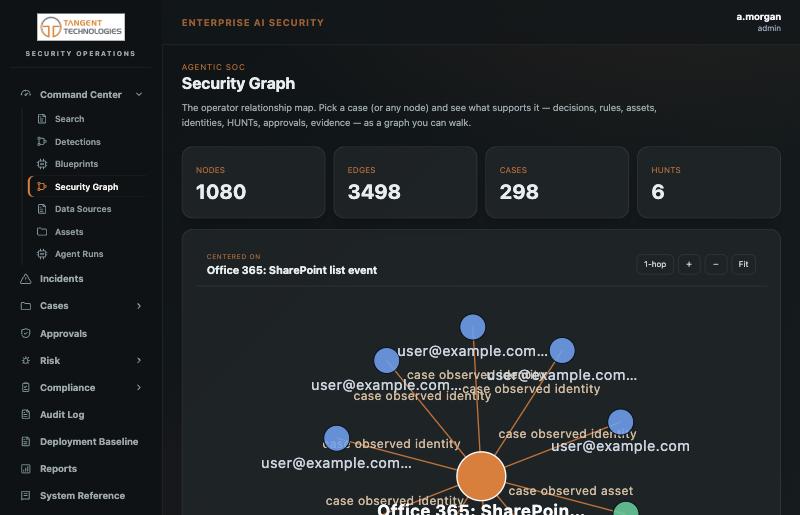
One case, every connection. 1,080 nodes and 3,498 edges relate a case to the decisions, rules, assets, identities, hunts, approvals, and evidence that support it, so an investigator walks the graph instead of guessing.
How it works
Connect your estate. Get one answer you can defend.
Connect
Read-only, app-scoped connections to Microsoft 365, Defender for Endpoint, Azure/Entra, and Wazuh. No agents to re-roll, no data to re-key.
Derive one truth
Deterministic authority modules resolve each fact once; LangGraph AI agents reason over that single source instead of re-deriving it five different ways.
Decide with you
High-impact actions route through a human-in-the-loop approval queue. The AI proposes and evidences; your team confirms. Autonomy is earned, not assumed.
Prove it
Every decision lands in the audit chain with its evidence attached and is exportable to the compliance and questionnaire workflows on demand.
Principles
The rules the platform refuses to break.
01Evidence over assertion
If the system can’t prove it, it says “insufficient evidence”. It never invents a control result or a clean bill of health.
02Telemetry over badges
Liveness and health come from real event flow and check-ins. A cosmetic vendor badge is a claim to verify, not a verdict.
03One source of truth
Every shared fact has exactly one authority. No fact lives in two places to drift apart and start disagreeing.
04Right-sized
The same console serves a solo CISO and a regulated enterprise, Commercial or on your own tenant, scaled to the team you have.
Get started
Bring one auditable truth to your security operations.
We’ll walk the Console against a real slice of your environment and show you what your current stack is leaving on the table: the blind spots, the silent drops, the facts that disagree.